Cyber Defense Strategies
The discovery of self-propagating "mind viruses" in August 2026 marked a pivotal shift in how security professionals approach the safety of autonomous artificial intelligence systems. These specialized digital pathogens do not target traditional code vulnerabilities but instead exploit
Implementing a network-layer kill switch provides security teams with an automated mechanism to instantly quarantine compromised devices or terminate connections without waiting for manual approval. As the proliferation of autonomous AI agents within corporate networks reaches unprecedented levels
The transition of CVE-2025-62593 into the Known Exploited Vulnerabilities catalog highlights a growing trend of attackers focusing on the foundational infrastructure of the AI era. This specific vulnerability targets the Ray framework, an open-source compute platform used extensively for scaling
Automated systems within the command-and-control infrastructure are currently processing and categorizing thousands of stolen archives, using specific naming conventions that link machine names to time-stamped files. This unprecedented level of organization underscores the sheer scale of the
Defensive strategies are shifting toward monitoring behavioral patterns like unauthorized credential access and mass file modifications to counter AI-driven threats. The rise of MessiahGPT marks a pivotal moment in this shift, as the tool represents a specialized, adversarial large language model
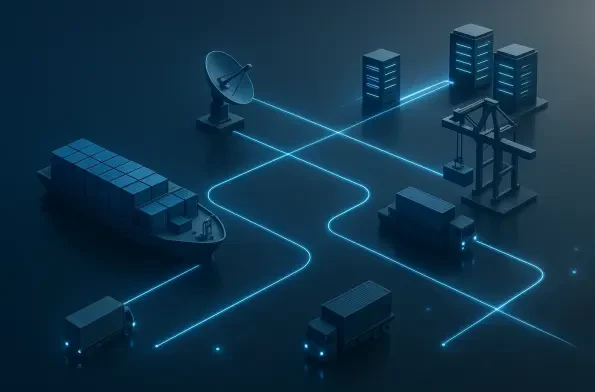
The maritime industry currently faces a ticking financial time bomb due to systemic underfunding of digital defenses compared to land-based enterprises of similar scale. As global trade becomes increasingly reliant on automated port logistics and satellite-linked navigation systems, the
Read More