Operational governance requires the continuous monitoring of all model requests and outputs to detect unusual patterns that might indicate a breach. As artificial intelligence transitions from a specialized tool to a foundational business utility, a significant change in deployment strategy is taking place across the global market. Industry projections suggest that by the end of 2026, nearly half of all enterprises will integrate open-weight models into their production environments. While this transition offers organizations greater autonomy and improved data security, it has also created a pronounced governance gap. This gap represents the disconnect between the rapid adoption of powerful, locally hosted models and the internal frameworks necessary to manage the unique risks they introduce. To succeed in this landscape, companies must transition from a consumer mindset to a custodian mindset, taking full responsibility for the lifecycle of their AI assets. This move requires a departure from traditional software oversight and the adoption of a proactive stance toward model integrity and long-term operational resilience.
The Evolution of Deployment and Local Control
Comparing Service Models: Renting Versus Owning
The modern AI landscape is defined by two primary paths: renting capabilities through provider-hosted services or owning them through open-weight deployments. When an organization rents a model via a standard software-as-a-service application, the provider manages the heavy lifting of infrastructure, security updates, and safety filtering. However, this convenience often comes at the expense of data sovereignty. Utilizing external servers for sensitive tasks, such as processing proprietary financial documents or legal contracts, creates significant privacy concerns and risks long-term vendor lock-in. Furthermore, service providers can alter model behavior or pricing without notice, forcing sudden and often disruptive changes on the client that can break downstream applications or inflate budgets unexpectedly. This dependency creates a fragile ecosystem where the enterprise has little say in the fundamental technology powering its essential business processes and decision-making systems.
Building on the need for autonomy, open-weight models allow an organization to download the learned parameters—the weights that define the intelligence of the system—and run them on internal infrastructure. This approach ensures absolute control over proprietary data and enables the application of custom access rules tailored to specific departmental needs. Currently, these models are rapidly closing the performance gap with proprietary leaders, trailing them by only a few months in raw capability and reasoning power. However, this shift grants autonomy at a significant cost; the user must assume the full spectrum of operational and security responsibilities that were previously handled by the external vendor. The organization is no longer just a user of technology but the operator of a complex, probabilistic engine that requires constant maintenance and a deep understanding of the underlying architecture. This transition necessitates a robust internal talent pool capable of managing high-performance computing clusters.
Security and Infrastructure: Mitigating New Vulnerabilities
Open-weight AI is not a plug-and-play solution and introduces several distinct vulnerabilities that differ significantly from traditional software security models. Model files can be engineered as Trojan horses, designed to execute malicious code the moment they are loaded into GPU memory or a system environment. There is also the significant challenge of provenance, as models sourced from public repositories may have been modified by third parties to include hidden backdoors or weakened safety controls. Without a clear origin story and a verified digital fingerprint, an organization risks deploying a version that contains intentional flaws or security bypasses that could lead to data exfiltration. The complexity of these weights makes manual inspection nearly impossible, meaning that a compromised model can remain undetected for long periods while providing subtly biased or dangerous outputs. Consequently, the verification of model weights must become as rigorous as the auditing of financial statements or the scanning of traditional source code.
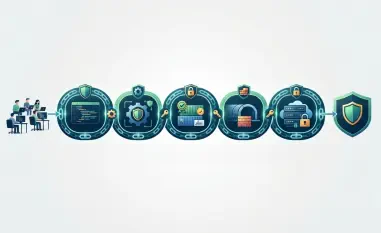
To address infrastructure burdens, organizations have developed model ledgers to record the source, version, and license of every asset, ensuring that all downloads are verified against trusted references. This proactive stance helps maintain the integrity of the AI lifecycle and provides a strategic advantage that is both secure and sustainable. Moving forward, the implementation of a unified strategy centered on accountability and integrity has become the industry standard. Every model is assigned a designated internal owner responsible for approving its use and overseeing incident responses. Rigorous “trust after testing” protocols are established before any model enters a production environment, including red-teaming exercises where models are treated as potential attackers. For high-risk applications, systems operate within sandboxed environments with restricted access to internal credentials. This comprehensive governance framework ultimately allows companies to transform their AI assets into resilient drivers of innovation while minimizing the risks of local deployment.