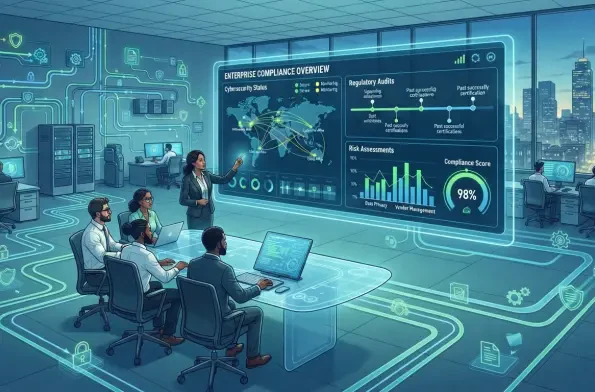
High-performing platforms now focus on multi-framework operations, allowing a single control to be mapped across dozens of different global security standards. The compliance environment has transitioned from a retrospective archaeological project into a proactive plumbing operation, where real-time connectivity replaces the manual excavation of historical records. Organizations no longer spend months digging through old logs or capturing static screenshots to satisfy an auditor’s request. Instead, modern infrastructure relies on persistent API connectors that integrate directly with cloud environments, human resources information systems, and device management protocols. This shift ensures that compliance is a living byproduct of daily operations rather than a disruptive annual event. By 2026, the standard for trust has moved toward continuous verification, where evidence is pulled automatically and validated against established benchmarks without human intervention. This transformation has not only reduced the administrative burden on engineering teams but has also heightened the overall security posture of the digital economy by making vulnerabilities visible the moment they arise. The current market emphasizes the importance of a unified data stream, ensuring that every security check is recorded as it happens, rather than being reconstructed months after the fact.
Evolutionary Shifts: The Move to Continuous Verification
The current market is defined by the “Crosswalk Premium,” a metric that measures how effectively a platform maps a single security control across multiple regulatory frameworks. In the current 2026 to 2028 cycle, organizations are increasingly looking to maximize their return on compliance investment by reusing up to 80% of their evidence for secondary and tertiary certifications. For instance, a company that has solidified its SOC 2 posture can now seamlessly transition into ISO 27001 or HIPAA compliance without starting from scratch. This level of efficiency is only possible through sophisticated mapping engines that recognize the overlap between disparate standards, such as access control or encryption requirements. By focusing on the underlying control rather than the specific certification, businesses can scale their operations into new global markets with significantly less friction than in previous years. This strategic approach allows security teams to maintain a lean structure while managing an ever-growing list of requirements, turning compliance into a scalable asset rather than a growing liability.
Furthermore, the industry has reached a consensus that mere readiness is no longer a sufficient target for modern enterprises. The primary differentiator among top-tier platforms is the implementation of real-time drift alerts, which notify administrators the moment a security control falls out of alignment with the required standard. If a private cloud storage bucket is accidentally made public, the system triggers an immediate warning rather than waiting for an annual audit to discover the lapse. This real-time visibility has effectively moved compliance to the front lines of the sales cycle, where “Trust Centers” allow prospective customers to view a live dashboard of a vendor’s security health. These centers automate the response to security questionnaires, which used to consume hundreds of labor hours each year. By providing transparent, verified data to prospects, companies are closing deals faster and building deeper levels of trust. The focus has shifted from proving that a company was secure at a specific point in the past to demonstrating that it is secure at this exact moment and will remain so in the future.
Market Leaders: Distinguishing Between Breadth and Depth
Vanta and Drata continue to lead the automation space, functioning as the primary benchmarks against which all other platforms are measured. Vanta has maintained its position through a massive integration catalog that connects to nearly every piece of software an organization might use. Its strength lies in its ecosystem gravity, providing a comprehensive “Trust Center” that serves as the public-facing evidence of a company’s integrity. For organizations scaling into complex and emerging fields like AI governance, Vanta offers a breadth of coverage that is difficult to match. The platform has evolved into more than just an automation tool; it is a central hub for security operations, allowing teams to manage vendor risk and privacy requirements alongside their standard certifications. This wide-angle view of the compliance landscape makes it the default choice for companies that need to manage a diverse array of digital assets across multiple global jurisdictions while maintaining a clear and accessible record of their security posture.
In contrast, Drata has carved out a dominant position by focusing on the technical depth of its automation and the granularity of its evidence collection. Its “adaptive automation” feature allows the platform to recognize changes in a company’s underlying infrastructure and adjust security tests accordingly, ensuring that the compliance framework evolves alongside the code. For highly technical teams that prioritize precision and a seamless workflow for auditors, Drata offers a level of depth that minimizes manual intervention. Its ability to map evidence to specific controls with extreme accuracy reduces the time spent in the “observation window” during Type II audits. The platform’s internal workflow tools are designed to facilitate a smooth relationship between the security team and the independent auditor, ensuring that every piece of evidence is presented in a clear, standardized format. This focus on technical excellence and auditor-friendly reporting has made it a favorite for organizations that view their security infrastructure as a competitive advantage and want to ensure that every detail is captured with total fidelity.
Enterprise Rigor: Solutions for Governance and Complexity
As organizations mature and move beyond their initial certifications, they often require the level of governance and discipline provided by AuditBoard and Hyperproof. AuditBoard, with its deep roots in internal audit and Sarbanes-Oxley compliance, is specifically designed for enterprise-level organizations that must report to a formal audit committee. It provides a level of rigor and structured oversight that smaller, startup-centric tools may lack. The platform excels at managing the complex interplay between internal controls, risk management, and regulatory requirements, making it an essential tool for companies operating in highly regulated industries like finance or healthcare. For these organizations, compliance is not just about passing a single test; it is about establishing a permanent operational discipline that protects the company’s reputation and financial stability. AuditBoard’s sophisticated reporting capabilities provide executives with the insights they need to make informed decisions about risk and resource allocation, ensuring that the compliance program is fully integrated into the broader business strategy.
Hyperproof offers a different but equally vital specialized capability by focusing on multi-framework operations for global enterprises. Its architecture is built around a control-centric model, where a single security control is managed in a central repository and then automatically applied to every relevant framework in the company’s portfolio. This approach is particularly effective for organizations that must maintain a dozen or more global certifications simultaneously. Instead of managing a separate project for each standard, teams can manage their entire compliance estate from a single dashboard. This reduces the risk of conflicting controls and ensures that evidence is used consistently across the entire organization. Hyperproof acts as the operational engine for complex, multinational compliance programs, providing the structure and automation necessary to manage thousands of different requirements without becoming overwhelmed. By focusing on the operational reality of managing global frameworks, it helps enterprises move from a state of reactive compliance to one of proactive governance, where every security measure is tracked and validated in real time.
Specialized Support: Paths for Velocity and Guidance
Organizations that lack extensive internal compliance expertise frequently turn to specialized solutions like Secureframe and Thoropass to bridge the gap. Secureframe differentiates itself by offering a hybrid model that pairs its sophisticated automation software with access to a fractional compliance team. This approach is particularly valuable for first-time certification seekers who may struggle with the initial scoping of their environment or the creation of complex security policies. By providing expert guidance alongside the software, Secureframe ensures that companies do not just automate their existing problems but instead build a solid foundation of security best practices. This hands-on support helps to demystify the compliance process, allowing small teams to achieve SOC 2 or ISO 27001 status with the same level of confidence as a much larger organization. The platform’s ability to act as both a tool and a consultant makes it an ideal choice for startups that need to move quickly but cannot afford to hire a full-time compliance officer.
For those seeking maximum convenience, Thoropass offers a bundled approach that combines the automation platform and the audit into a single contract. This model provides a streamlined path to certification, often referred to as “one throat to choke,” where a single vendor is responsible for the entire outcome. While this convenience is highly attractive to smaller startups focused on closing their first major enterprise deals, it does raise questions about the optics of auditor independence. Many larger enterprise buyers prefer a clear separation between the software that collects the evidence and the auditor who evaluates it to avoid any perception of a “self-graded” exam. Consequently, while Thoropass excels in providing a friction-free experience for early-stage companies, more mature organizations often opt for the “network model” favored by leaders like Vanta or Drata. These organizations use a platform to gather data but hire an independent third-party firm to conduct the final audit, maintaining the highest standards of objectivity and transparency required by the most demanding global clients.
Strategic Implementation: Verifying Resilience and Readiness
The transition to automated compliance platforms has fundamentally changed how organizations evaluate their readiness for an audit. In the current 2026 environment, a simple demonstration of software features is no longer sufficient; buyers are now performing rigorous “test drives” of platform connectors to ensure they function correctly within their specific technology stack. A critical part of this evaluation involves a “drift test,” where a security team deliberately breaks a control—such as disabling multi-factor authentication for a non-critical user—to see how quickly the platform detects and alerts the administrator. This proactive testing ensures that the automation is not just a passive collector of data but an active participant in the company’s security posture. Furthermore, organizations must still account for the fixed calendar constraints of a Type II audit, which requires several months of data to prove operational consistency. Even the most advanced software cannot bypass the time required to demonstrate that security controls have been working effectively over a sustained period.
The 2026 market underscored the necessity of viewing security not as a hurdle to be cleared, but as a foundational utility. Organizations that prioritized the separation of software from auditing services generally achieved a higher level of trust with their most scrutinized enterprise partners. The transition toward automated plumbing effectively eliminated the chaotic surges of activity that once preceded annual renewals, allowing security teams to maintain a steady state of readiness throughout the fiscal year. Moving forward, the focus shifted toward the integration of artificial intelligence governance within these existing frameworks, as companies realized that a single, unified control environment offered the most resilient defense against emerging digital threats. By establishing these persistent automated systems, businesses moved beyond the era of static certifications and entered a phase of continuous operational excellence that redefined the meaning of corporate accountability in the digital age. This progress ensured that the relationship between security, compliance, and business growth remained stronger and more transparent than ever before.