Vulnerability Assessment
The emergence of a critical vulnerability within the F5 BIG-IP Access Policy Manager has triggered an urgent call for immediate remediation across the global cybersecurity landscape. This specific flaw, tracked as CVE-2025-53521, represents a severe threat because it allows unauthenticated
The rapid escalation of cyber threats in 2026 has brought a critical vulnerability in Fortinet’s FortiClient Endpoint Management Server to the forefront of enterprise security concerns. This flaw, identified as CVE-2026-21643, presents a severe risk because the affected software acts as a central h
Maintaining the integrity of a secure perimeter requires constant vigilance because even the most trusted tools can harbor silent vulnerabilities that threaten to collapse an entire network's availability. StrongSwan remains a cornerstone of the open-source security world, providing essential
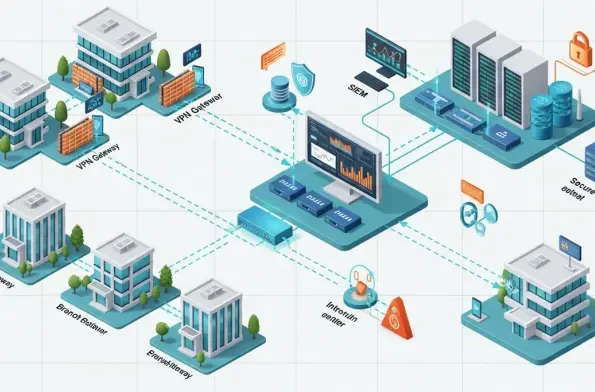
Malik Haidar stands at the forefront of modern cybersecurity, specializing in the complex intersection of artificial intelligence and enterprise infrastructure. With a background that spans deep threat intelligence and strategic security leadership for multinational corporations, he has spent years
The rapid proliferation of sophisticated algorithmic threats has forced a total reevaluation of how global financial institutions protect their most sensitive data assets. As the boundary between traditional banking and digital infrastructure continues to blur, the integration of Artificial
The sudden appearance of a public exploit for a critical server vulnerability acts as a starter pistol for a race that security teams can rarely win without prior preparation. When the CVE-2026-21962 vulnerability in Oracle WebLogic Server surfaced, it carried the maximum possible severity rating
Read More