The reintroduction of verbal passwords marks a significant reversal of the decade-long industry push toward automated and passwordless authentication systems. In an era where generative artificial intelligence has achieved nearly perfect mimicry, the psychological weight of a familiar voice is no
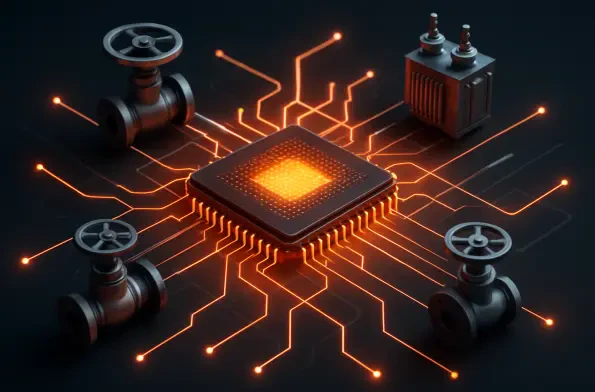
The convergence of digital and physical risk means that a breach in an operational technology environment can now result in the mechanical failure of heavy machinery and pumps. The contemporary cybersecurity environment is undergoing a fundamental and dangerous transformation as the focus shifts
The shift from lone-wolf hackers to highly organized project managers marks a profound transformation in how digital extortion and espionage are conducted in 2026. This year, the professionalization of the industry reached a peak where actors no longer build every tool themselves but instead act as
The breach of critical infrastructure by Salt Typhoon highlights a dangerous weakness in the mandatory access points used by law enforcement for digital wiretapping. This incident demonstrates that once a digital entry point is created, it becomes an irresistible target for state-sponsored hacking
Security researchers have identified a macOS Spotlight memory leak that allows malicious applications to exfiltrate sensitive user data through specially crafted PostScript files. This discovery highlights a fundamental shift in how vulnerabilities are perceived, as even the most integral
Geographic distance no longer offers a shield against cyber warfare because globalized infrastructure ensures that regional conflicts have immediate, worldwide digital consequences. The traditional mental model that separated physical battlefields from digital domains has disintegrated, leaving
Identity-based attacks frequently begin with device code phishing, where attackers trick users into providing OAuth tokens to gain the authorization needed for rogue device registration. This sophisticated approach represents a fundamental shift in the cyber-threat landscape, moving away from