The Evolving Landscape of Frontier AI and Conversational Security The illusion of foolproof artificial intelligence often shatters when a simple interaction transforms into a persistent, multi-layered dialogue designed to bypass the most rigorous safety protocols. As the generative AI industry
The Dawn of Operation Saffron: A Watershed Moment in Cyber Enforcement The digital landscape shifted fundamentally when an international coalition of law enforcement agencies successfully penetrated the encrypted shadows of the dark web’s most trusted sanctuary. In a landmark achievement for i
Small and medium-sized businesses are currently grappling with an unprecedented surge in sophisticated automated attacks that utilize machine learning to bypass traditional perimeter defenses within seconds. This shift has fundamentally altered the defensive posture of organizations that previously
The relentless cadence of modern digital life often masks the silent battles occurring within the silicon and software that power our global economy. When Microsoft engineers pulled the metaphorical lever for the May security update, they did more than just release a standard set of patches; they
The rapid convergence of generative modeling and automated penetration testing has created a digital environment where traditional security perimeters are failing faster than manual teams can respond to incoming alerts. In light of this, the Information Commissioner’s Office (ICO) has published a d
The recent confirmation of a massive data breach at Checkmarx has sent shockwaves through the cybersecurity community, highlighting how even the most fortified application security leaders can fall victim to sophisticated supply chain incursions. This incident serves as a stark reminder that even
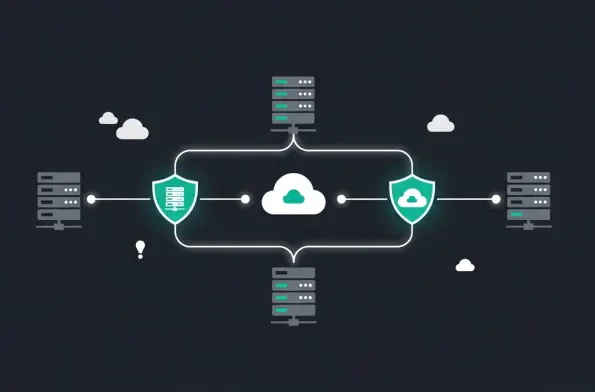
Security protocols that govern modern cloud ecosystems often rely on the absolute precision of administrative roles, yet even a minor oversight in permission boundaries can inadvertently grant a malicious actor total dominion over an entire organizational tenant. This reality became evident with