Vulnerability Assessment
The seamless integration of smart technology into the modern South Korean home has transformed daily convenience into a potential liability as sophisticated cyberattacks bypass traditional defenses with alarming ease. While the domestic Internet of Things market has ballooned to an estimated
The digital infrastructure that connects billions of users to their favorite services often relies on a fragile web of third-party scripts that operate silently in the background of every browsing session. This fragility was recently exposed through a major cybersecurity incident known as the
The modern expectation of digital privacy hinges on the assumption that a device's hardware components remain inaccessible to third-party software unless explicit, high-level permissions are granted by the user through a robust security framework. However, CVE-2026-65339 proved that even the
Threat actors are currently chaining an authentication bypass with a command injection flaw to gain complete root access to Barracuda Email Security Gateway appliances. This urgent warning comes as the Cybersecurity and Infrastructure Security Agency (CISA) added six vulnerabilities to its Known
Achieving high levels of accuracy in vulnerability management now requires a standard of deep, credentialed access rather than simple unauthenticated pings. In the current digital climate, security leaders face a landscape defined by extreme network segmentation and the complex fusion of
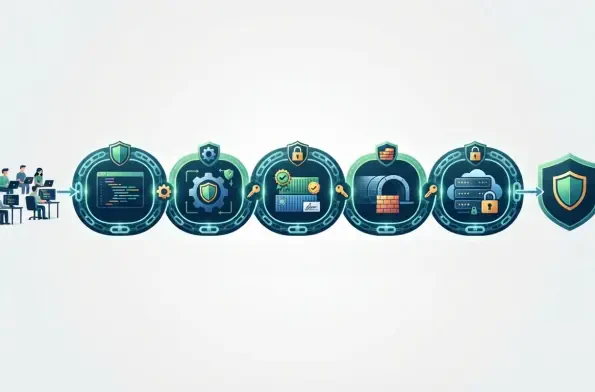
Finite State provides a truth-based view of a product’s security posture by analyzing the actual code that ships on hardware rather than just the design plans. This methodology has proven vital as the company secures a $27 million Series C funding round to fortify the global software supply chain. L
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 82 83 84 85 86 87 88 89 90 91 92 93 94 95 96 97 98 99 100 101 102 103 104 105 106 107 108 109 110 111 112 113 114 115 116 117 118 119 120 121 122 123 124 125 126 127 128 129 130 131 132 133 134 135 136 137 138 139 140 141 142 143 144 145 146 147 148 149 150 151 152 153 154 155 156 157 158 159 160 161 162 163 164 165 166 167 168 169 170 171 172 173 174 175
Read More