Cyber Risk Management
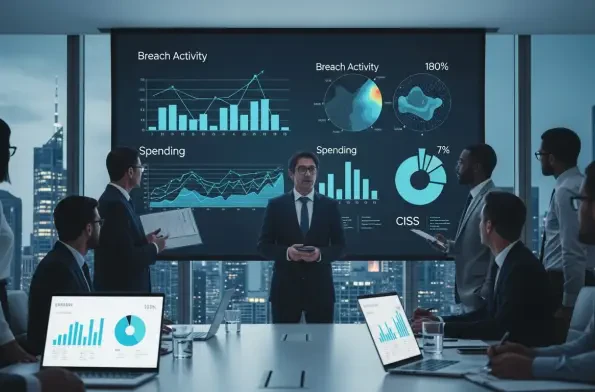
Market Context and Purpose Breach headlines multiply while payrolls barely inch forward, creating a whiplash market where risk soars as rewards stall and the professionals holding the line feel chronically underpaid. The security function has become a dependency for boards and regulators, yet
Stephen Morai sits down with Malik Haidar, a seasoned cybersecurity leader whose work blends hands-on reverse engineering with business-first risk strategy. With years spent countering sophisticated adversaries in multinational environments, Malik unpacks the rediscovery of fast16—a 2005-era s
Boardrooms cheered record AI rollouts while basic safeguards frayed, and attackers quietly slipped through reopened cracks. The tension between speed and security was no longer theoretical; it was surfacing in real incidents where sanctioned AI projects stumbled on fundamentals long considered
Malik Haidar has spent years in the trenches of multinational security, closing the distance between boardroom priorities and frontline incident response. He treats identity not just as a login but as a living system spanning humans, non-human services, and fast-moving agentic AI. In this
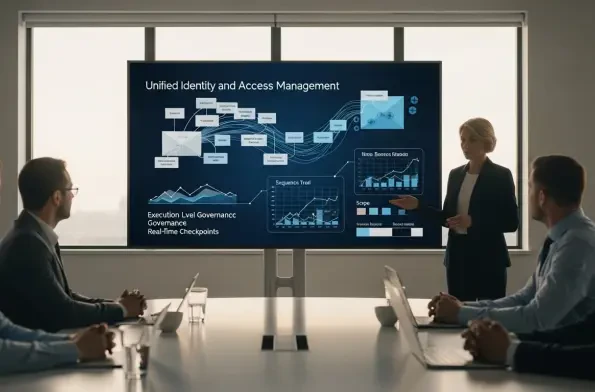
Malik Haidar has spent years inside multinationals translating threat intelligence into boardroom-ready decisions, bridging analytics with business impact. In this conversation with Jason Costain, he unpacks what an early, Lua‑powered sabotage platform reveals about state priorities, how k
Why Fixes to Security Tools Matter Now: Context, Stakes, and What This Story Covers Breaches often begin where trust is highest, and security platforms sit closest to the crown jewels, so a single unpatched flaw can flip defenses into conduits for stealthy data access, lateral movement, and
Read More