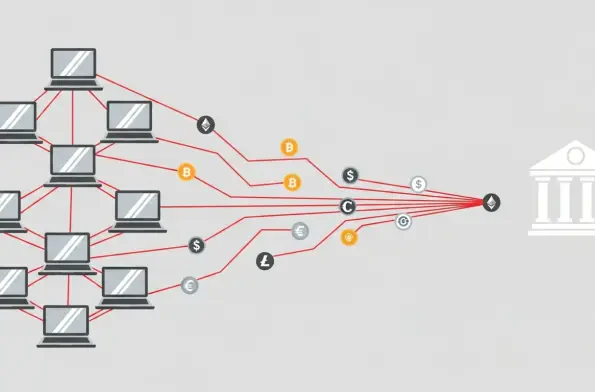
In the shadowy theaters of modern geopolitical conflict, a new and alarming model of state-sponsored aggression has taken root, blurring the lines between ideologically driven hacktivism and financially incentivized cyber warfare. A pro-Russian hacker collective has refined a strategy that
The familiar red flags of cyber scams, such as glaring grammatical errors or suspicious sender addresses, are rapidly becoming relics of a bygone era as criminals now wield powerful artificial intelligence tools to craft attacks with unprecedented sophistication. What used to be easily identifiable
The digital perimeter that once clearly defined corporate security has dissolved into a complex and borderless ecosystem, placing an unprecedented burden on the very tools designed to protect it. In this new reality, the Next-Generation Firewall (NGFW) has evolved from a simple gatekeeper into the
The recent debut of the VolkLocker ransomware platform serves as a stark reminder that in the world of cybercrime, a threat's potential for destruction is not always matched by the sophistication of its design. The Ransomware-as-a-Service (RaaS) model continues to lower the barrier to entry
The year 2025 will be remembered as the moment cybersecurity crossed an irreversible threshold, a point of no return where the integration of Artificial Intelligence into the fabric of digital conflict became absolute. This pivotal period marks a distinct "before-and-after" in the
What began as a critical but broadly exploited software vulnerability has quietly transformed into a sophisticated tool for state-sponsored espionage, signaling a dangerous escalation in the strategic use of widespread security flaws. The exploitation of the React2Shell vulnerability now serves as
A critical security flaw within the widely-used WinRAR file compression utility has been transformed into a potent weapon for state-sponsored cyber espionage groups, prompting an urgent directive from U.S. cybersecurity authorities. The vulnerability, tracked as CVE-2025-6218, is a path traversal